Access note
ID 001
Current focus
Red Team operations, vulnerability research, and secure system architecture, backed by full-stack product development with TypeScript, React, Go, FastAPI, and cloud-native tooling.
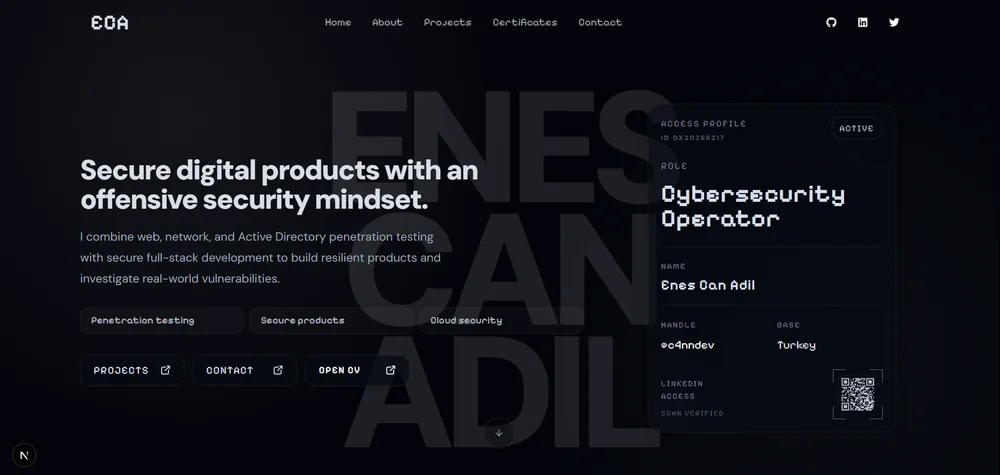
Secure digital products with an offensive security mindset.
I combine web, network, and Active Directory penetration testing with secure full-stack development to build resilient products and investigate real-world vulnerabilities.
About
I am a cybersecurity specialist and full-stack developer based in Turkey, primarily focused on Red Team operations, vulnerability research, and secure system architecture.
I pair that offensive mindset with Blue Team foundations gained during an enterprise Security Operations Center internship. My work spans web, network, and Active Directory penetration testing, CVE discovery with USOM-oriented reporting, malware analysis fundamentals, and secure end-to-end application development with React, TypeScript, Go, FastAPI, Docker, Cloudflare Workers, and AWS fundamentals.
Beyond hands-on technical work, I contributed to the cybersecurity community through Ankara University AUSTIN, where I helped coordinate technical workshops, trainings, CTF events, and practical learning experiences for students.
Access note
ID 001
Current focus
Red Team operations, vulnerability research, and secure system architecture, backed by full-stack product development with TypeScript, React, Go, FastAPI, and cloud-native tooling.
Access note
ID 002
Research
Two assigned CVEs — CVE-2026-13696 (LDAP injection) and CVE-2026-6217 (unsalted password hashing) — both disclosed through TR-CERT / USOM coordination.
Access note
ID 003
Practice
Completed 200+ practical labs across TryHackMe and Hack The Box, including web, network, Linux, and Active Directory attack paths.
Skills
01
Web, network, and Active Directory penetration testing; vulnerability research and CVE discovery, privilege escalation, and bug bounty operations.
02
Threat monitoring, incident response, log analysis, network traffic inspection, and fundamental malware analysis.
03
Full-stack development with Go, FastAPI, React, and TypeScript, focused on secure coding (OWASP), API security, and Flutter mobile development.
04
AWS fundamentals, Cloudflare edge computing, server hardening, and Docker containerization.
Certifications
Education
2026 – Present
Bachelor's Degree in Management Information Systems
Interdisciplinary program combining business administration principles with information technology and system architecture.
2023 – 2026
Associate Degree in Cybersecurity Analysis and Operations
English-medium program focused on network security, Red Team operations, and incident response. Graduated with a GPA of 3.43 / 4.00.
Experience
Jan 2026 – Sep 2026
Promoted to a contracted Cybersecurity Specialist after months of high-impact volunteer vulnerability research. Executed penetration tests and offensive security assessments on community-facing platforms, and led the design of a secure, scalable architecture for the CyberMap ecosystem.
Feb 2026 – Jun 2026
Worked inside enterprise-level Security Operations Center workflows and defense strategies, assisting with daily threat monitoring, incident response, and system hardening procedures.
2025 – 2026
Organized cybersecurity trainings, workshops, and CTF events for the student community while managing technical content development.
2024 – 2025
Managed IT infrastructure, systems support, and technical troubleshooting for the Vocational School of Cybersecurity.
2022 – 2023
Şehit Murat Bulkan MTAL
Completed a one-year long-term internship focused on foundational IT operations, hardware maintenance, and basic cybersecurity practices.
Research
Vulnerabilities I discovered in production software and disclosed responsibly through TR-CERT / USOM coordination, each assigned a public CVE identifier after vendor remediation.
CVE record
ID 001
LDAP Injection · CWE-90
Insufficient input sanitization allowed LDAP queries to be manipulated, opening the door to authentication and directory data abuse. Reported and remediated before public disclosure.
CVE record
ID 002
Unsalted Password Hashing · CWE-759
Stored credentials were hashed with a one-way function but no salt, leaving password material exposed to pre-computation and cryptanalysis attacks. Reported and remediated before public disclosure.
Projects
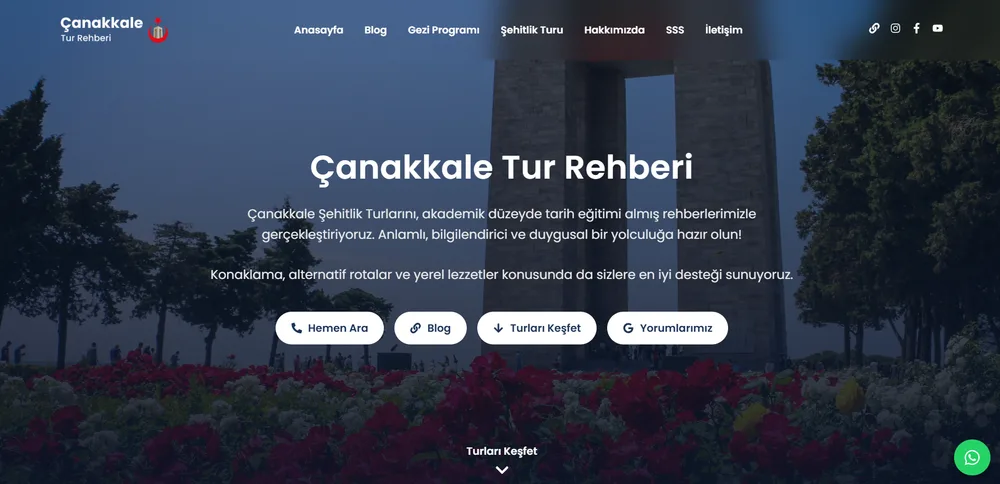
Selected web products, security-focused utilities, dashboards, and automation experiments shaped by secure architecture, maintainable code, infrastructure awareness, and practical decisions from real-world cybersecurity work.
 01
 02
 03
 04
 05
 06
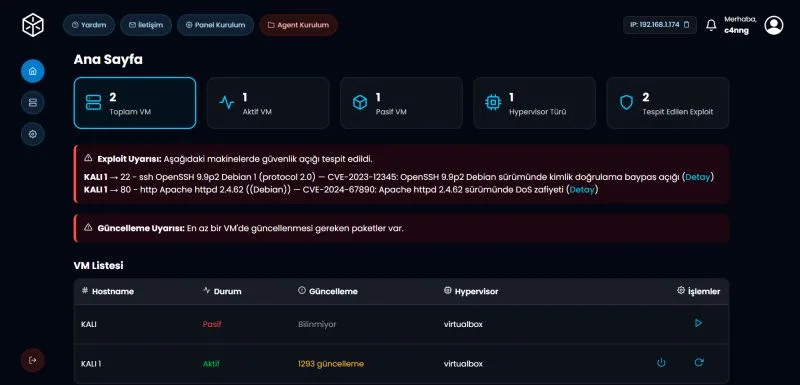
Secure dashboard interface for managing virtual machines and operational system views, built as an internal tool.
Certificates
Certifications and lab-based progress supporting my offensive security path across junior and professional penetration testing, cloud security fundamentals, API security, practical labs, and ongoing OSCP preparation.
Access card
ID 001
APIsec Certified Practitioner - APIsec University
On file
Certified Cloud Associate - INE
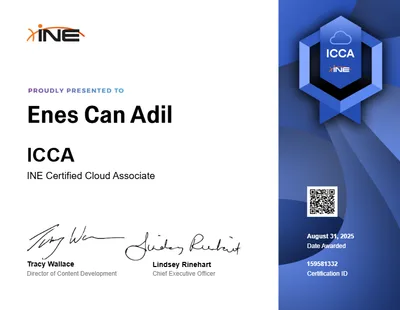
Verified
Pro. Penetration Tester - INE
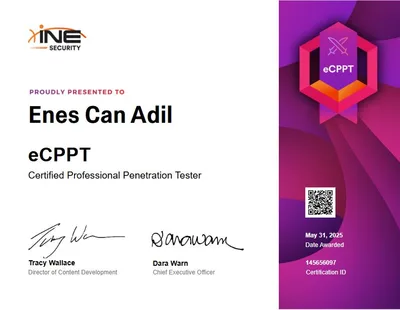
Verified
Junior Penetration Tester - INE
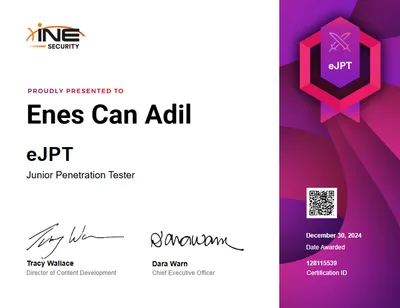
Verified
Junior Penetration Tester - THM
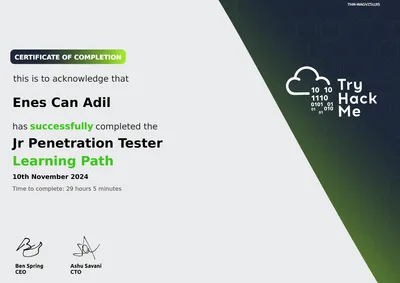
Verified
Contact
Reach out for penetration testing conversations, secure full-stack product work, vulnerability research collaboration, cybersecurity community projects, or technical workshops focused on practical cybersecurity work.